Offline License Verification Has a Local Trust Limit
Understand how offline license signature verification works in browser extensions, what belongs in the signed payload, and why client-side runtimes have local trust limits.
Engineering secure browser extensions for Chrome, Firefox, and Edge: Manifest V3 migrations, DOM automation, sandbox permissions, and store compliance.
Understand how offline license signature verification works in browser extensions, what belongs in the signed payload, and why client-side runtimes have local trust limits.
Learn how to build a zero-API publishing extension for platforms with deprecated write APIs by leveraging active browser sessions and contenteditable DOM injection.
A practical guide to architecting sustainable browser extension monetization while respecting privacy policies, store compliance, and user security.
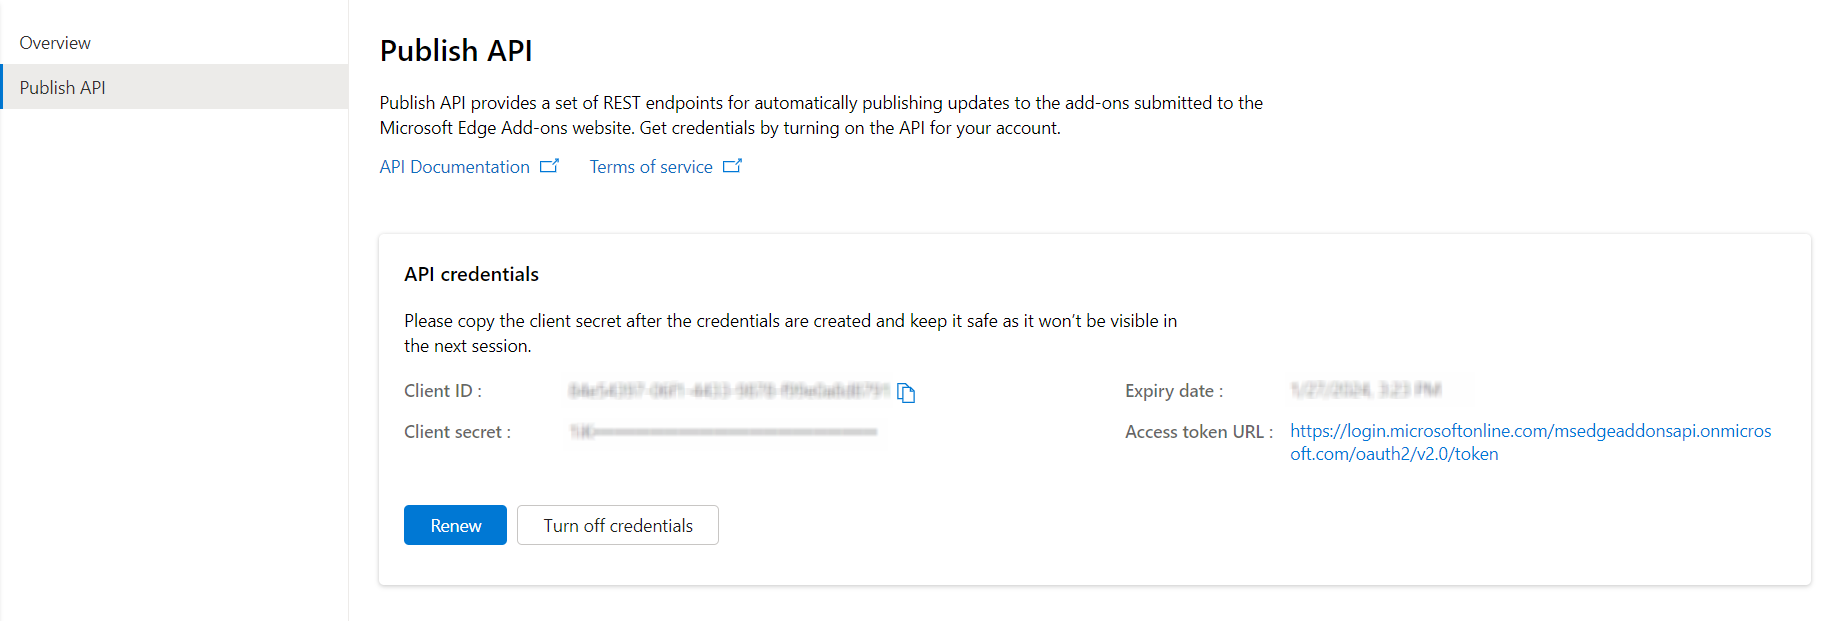
Build one browser extension release pipeline with reproducible archives, store-specific APIs, safe credentials, bounded retries, and independent publication verification.